A perspective piece from The Listening Market
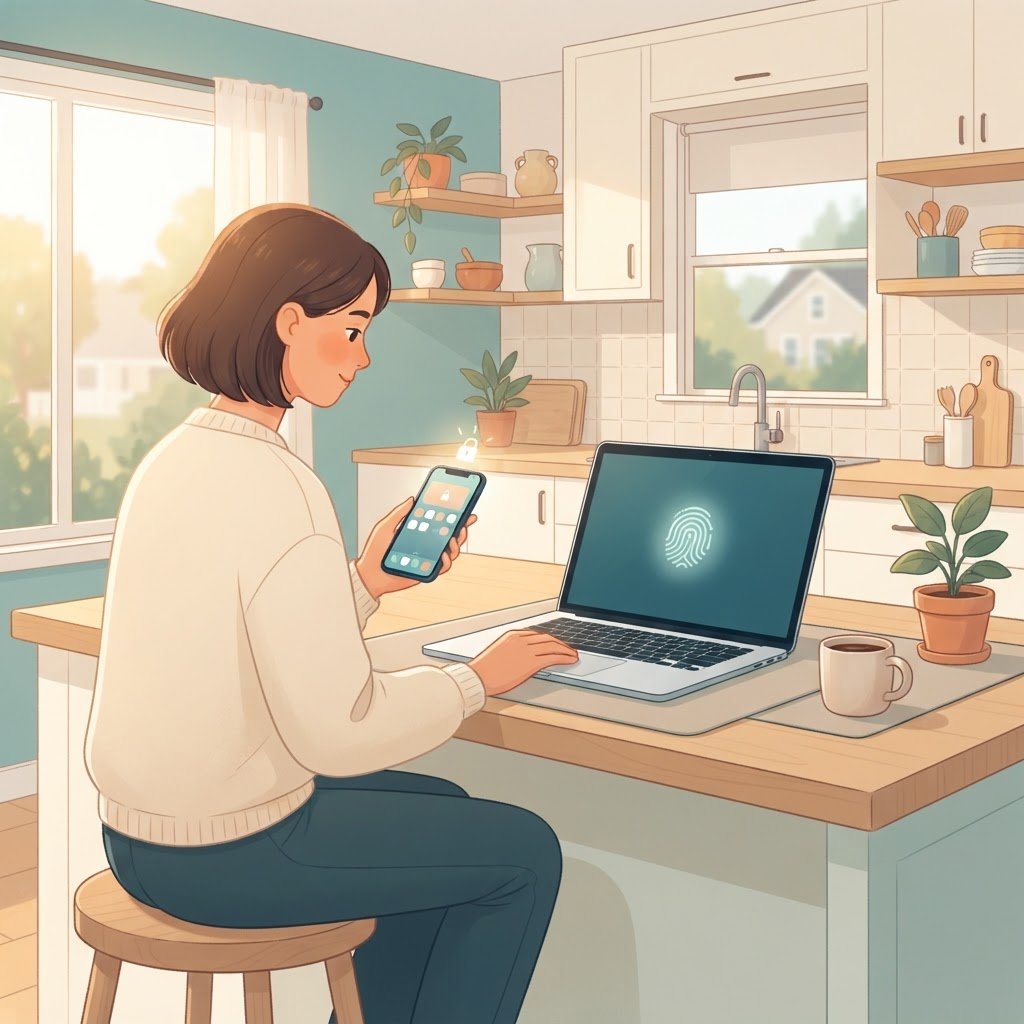
The moment usually passes without ceremony. A person sits down at a laptop, navigates to a website they have not visited in months, and instead of the familiar dance of forgotten passwords and recovery emails, a small window appears asking them to unlock their phone. One tap, one glance at the screen, and they are in. No password was typed. No password even exists. The login that used to take four minutes now takes four seconds, and the strange thing is how quickly it has stopped feeling strange.
Passwordless sign-in has quietly crossed the line from novelty to default. For two decades, the password was the load-bearing wall of digital life, and everyone tolerated its cracks. Now the wall is being dismantled, one service at a time, and the shift is happening so gradually that most people have never paused to notice that the most hated ritual of the internet is disappearing.
The problem nobody could solve
The case against passwords has been open for years. They are easy to guess, easy to reuse, and easy to steal. Security researchers have repeated the same uncomfortable statistics so often that they have lost their sting: most people hold dozens of accounts but recycle a handful of passwords across all of them, and a large share of those passwords could be cracked by a consumer graphics card in an afternoon. The password’s greatest weakness was never technology. It was human memory, which was never designed to store a hundred random strings of characters and was always going to improvise.
The industry’s first answer was to bolt things on. Password managers arrived, promising a vault for the chaos, and they genuinely helped the people who adopted them. Two-factor authentication added a second lock on the door, usually a code sent by text message. But both of these treated the password as a fact of life rather than a design choice. The login still began with something you know, and anything you know can be phished, coaxed out of you, or pulled from a breached database sitting on a dark web marketplace.
Every year, billions of credentials are spilled in breaches, and every year a fresh wave of ordinary people discover that an account they forgot they owned has been used for fraud. The password had become a tax on the whole internet, paid in lockouts, reset emails, and quiet losses. What was missing was a way to prove identity without asking anyone to remember anything at all.
How passkeys changed the equation
The breakthrough came not from a single company but from an unlikely alliance. Apple, Google, and Microsoft, competitors who rarely agree on anything, sat down with the body that governs web standards and settled on a shared approach called passkeys. The idea is disarmingly simple. When an account is created, the device generates a pair of cryptographic keys. One half, the private key, never leaves the phone or computer, protected by the same fingerprint or face scan that unlocks the screen. The other half is registered with the website. Logging in becomes a handshake rather than a quiz. The site issues a challenge, the device signs it, and the user simply proves they are holding the right device with a biometric glance.
The beauty of the system is what disappears. There is no secret transmitted over the network, so there is nothing for a hacker to intercept. There is no shared secret stored on a company server, so there is nothing to leak when that server is breached. A phishing site that looks identical to a bank’s login page cannot use a passkey, because the cryptography is bound to the genuine domain. The most common attacks of the last decade, credential stuffing and phishing, simply bounce off.
Adoption has moved faster than with almost any security technology before it. The big platforms began rolling out passkey support and made the option unavoidable, sometimes to the annoyance of users who preferred the old rituals. Major banks, retailers, and government services followed. Within a few seasons, hundreds of millions of accounts had been upgraded, most of their owners barely aware of the cryptography humming beneath the tap of a thumb. That invisibility is precisely the point. Security that requires effort from the average person tends not to survive contact with the average person. Security that happens as a side effect of unlocking a phone has no such trouble.
What it means for everyday life
For individuals, the change shows up as small returns of time and peace of mind. The reset email becomes rare. The anxious inventory before a trip, trying to remember which password unlocks the airline app, loses its edge. Accounts stop being hostages. People who once wrote passwords on sticky notes, or in notes apps far less secure than they imagined, find the whole category of worry quietly retired.
For businesses, the maths is blunt. Password resets have long consumed enormous volumes of support desk time, and stolen credentials are the leading opening move in most data breaches. Removing the password removes the costliest ticket in the queue and the most common key in the intruder’s toolkit. It is rare for a security decision to be simultaneously good for the bottom line, good for the customer, and good for the attacker’s frustration levels, which is partly why the shift has felt less like a debate and more like a tide.
There are honest caveats. Losing the device that holds the passkeys needs to be recoverable, which is why the platforms built syncing and backup into the design, and why a spare recovery method still matters. Some services offer passkeys as an option while quietly keeping password login alive behind it, so the old attack surface shrinks but does not vanish overnight. And the systems that tie identity to a single corporate ecosystem raise fair questions about lock-in and portability, questions the standards bodies are still working through in public.
The part nobody sees
Behind the scenes, the shift is being felt most strongly in the parts of the economy that were drowning in the old system. Enterprise IT departments, which once spent vast sums on password resets and on the identity chaos of contractors and temporary staff, have been among the fastest movers, equipping employees with hardware security keys that take the passkey principle to its most durable extreme. A small device that must be physically present defeats remote attackers no matter how clever the phishing kit, and after a wave of high-profile intrusions that began precisely with stolen credentials, security teams stopped treating the upgrade as optional.
The recovery experience, the unglamorous art of getting back in after a phone is lost in a river, has received equal attention. Early versions of passwordless systems made recovery the weak link, a back door guarded by the same flimsy knowledge questions the industry was trying to escape. The mature implementations now spread recovery across devices and trusted contacts, so that losing one phone is an inconvenience rather than an identity crisis. It is the part of the design users hope never to test and can be grateful was not left as an afterthought.
The quiet default
What makes this moment notable is not the technology itself but the trajectory. Security revolutions usually begin with warnings and end with a minority of diligent adopters. This one began with the platforms, who absorbed the complexity and handed users a simpler experience than what it replaced. Nobody had to be lectured into using passkeys. They simply found that logging in had become a tap, and they kept tapping.
It offers a lesson wider than login screens. The problems that persist in digital life persist not because solutions are impossible but because the solutions ask too much of human nature. The password asked people to be databases, and people are not databases. The replacement asks them to do something they were already doing dozens of times a day, unlocking a phone, and folds the security into the gesture.
The next time a login happens with nothing typed and nothing remembered, it may be worth a small pause of recognition. One of the internet’s oldest and most hated inventions is being retired not with a grand announcement but with a shrug, and the retirement party is happening on every screen, one silent tap at a time.